

Quick answer: Secure e-commerce migration in 2026 mandates a 'security-first build' approach, focusing on end-to-end data encryption, robust access controls, continuous threat monitoring, and adherence to evolving compliance standards like PCI DSS and GDPR to prevent data breaches and reputational damage.
Key takeaways
- A 'security-first build' philosophy is crucial for e-commerce migration, mitigating risks like data breaches, downtime, and reputational damage.
- Comprehensive pre-migration planning, including platform auditing, goal definition, data mapping, and risk assessment, forms the foundation of a secure transition.
- Data integrity and security during migration require secure extraction, encryption (in transit and at rest), strong access controls, data validation, and compliance adherence.
- Continuous testing (penetration, vulnerability, UAT) and ongoing post-migration security monitoring are essential for maintaining a secure e-commerce environment.
- Future e-commerce security will increasingly rely on AI/ML, passwordless authentication, supply chain security, and preparedness for quantum computing threats.
The Imperative of Secure E-commerce Migration in 2026
In 2026, a secure e-commerce migration is not merely an option but a critical necessity for any online business. This process involves moving an e-commerce platform from one hosting environment or software to another while safeguarding all data and functionalities. Non-negotiable security considerations for e-commerce migration in 2026 include end-to-end data encryption (in transit and at rest), robust access controls, continuous security monitoring and incident response systems, regular penetration testing, and stringent adherence to compliance standards such as PCI DSS, GDPR, and CCPA. An insecure migration risks severe data breaches, extensive downtime, and irreversible reputational damage, making a “security-first build” approach paramount from concept to deployment.
The digital landscape continues to evolve, presenting new threats to online businesses. Cyberattacks are growing in sophistication and frequency, with a reported 29% increase in cyberattacks globally in the first half of 2023, according to Check Point Research. For e-commerce platforms, this translates to heightened risks of customer data theft, financial fraud, and service interruptions. A secure e-commerce migration ensures that businesses do not inherit or create new vulnerabilities during a critical transition.
360Locker, founded on January 1, 2020, emphasizes a “security-first build” philosophy. This approach integrates cybersecurity measures from the very initial design stages through to deployment and ongoing maintenance. This proactive strategy is vital during migration, minimizing risks before they can be exploited. Without this focus, businesses face potential data breaches, significant downtime, and severe damage to customer trust and brand reputation.
Phase 1: Pre-Migration Planning and Assessment (The Foundation)
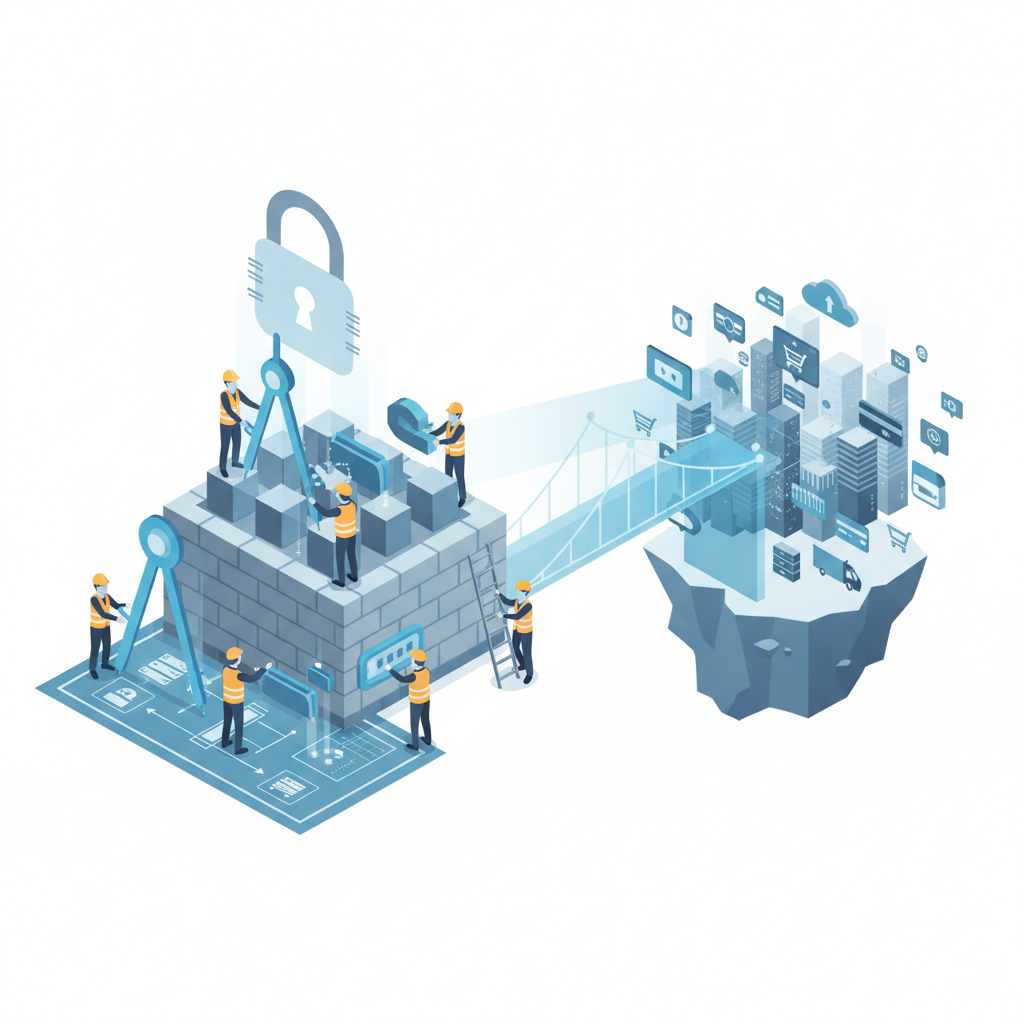
A robust pre-migration security audit is the cornerstone of any successful and secure e-commerce migration. It involves auditing the current e-commerce platform and infrastructure for vulnerabilities, defining clear migration goals that include security enhancements, thoroughly mapping all critical data points, selecting secure destination platforms and tools, and conducting a comprehensive risk assessment with mitigation strategies. This initial phase sets the stage for a seamless and secure transition, ensuring that potential issues are identified and addressed proactively.
Auditing the current e-commerce platform involves a deep dive into its existing infrastructure, code, and configurations. This helps identify any inherent security weaknesses or outdated components that could pose a risk during or after migration. Understanding the current state is crucial before moving to a new environment.
Defining clear migration goals is essential. These goals might include upgrading to a more scalable platform, enhancing overall security posture, or improving customer experience. For newcomers in the web world, 360Locker provides initial consultation and strategy formulation, guiding them through these complex decisions. Their expertise ensures that security is integrated into these goals from the outset.
Data mapping involves identifying all critical data points, such as customer information, order history, and product details. This process ensures that no essential data is overlooked during the transfer. Choosing the right destination platform and tools is equally vital, opting for solutions known for their robust security features and compliance certifications. Platforms like Shopify Plus or Magento offer various security layers, but their implementation must be secure.
Finally, a thorough risk assessment helps identify potential threats and vulnerabilities specific to the migration project. Developing mitigation strategies for these risks reduces the likelihood of issues arising during the actual migration. This proactive planning is a hallmark of 360Locker’s approach, ensuring a solid foundation for secure e-commerce migration.
Phase 2: Data Integrity and Security Protocols During Migration
To ensure data integrity and prevent data loss during e-commerce migration, businesses must employ secure data extraction methods and tools, encrypt all data both in transit and at rest, implement robust access controls, meticulously sanitize and validate data for the new platform, and adhere to compliance requirements like PCI DSS and GDPR. This phase focuses on the actual movement of data, emphasizing protective measures at every step.
Secure data extraction methods prevent unauthorized access or manipulation of data as it’s being prepared for transfer. This often involves using secure APIs or authenticated database access. Once extracted, all data must be encrypted, both when it is being moved (in transit) and when it is temporarily stored (at rest). Data encryption is a fundamental cybersecurity measure that scrambles data, making it unreadable to unauthorized parties.
Implementing robust access controls ensures that only authorized personnel can access sensitive data during the migration process. This involves strong authentication mechanisms, such as multi-factor authentication (MFA), and role-based access permissions. According to a Microsoft Security report, MFA can prevent over 99.9% of automated attacks.
Sanitizing and validating data for the new platform involves cleaning up old, irrelevant, or corrupted data and ensuring that all transferred data conforms to the new platform’s structure and requirements. This step is critical for data integrity and system performance. Compliance considerations are also paramount; adherence to standards like PCI DSS (Payment Card Industry Data Security Standard) and GDPR (General Data Protection Regulation) is legally required and builds customer trust. PCI DSS ensures secure handling of credit card information, while GDPR protects personal data for EU citizens.
360Locker ensures “360-degree security” throughout this phase. Their comprehensive approach means that every aspect of data handling, from extraction to validation, is secured against potential threats, providing peace of mind to clients, especially newcomers in the web world.
Phase 3: Building and Testing the New Secure E-commerce Environment
Building the new platform with a “security-first build” mindset ensures that security is an inherent feature, not an add-on. A ‘security-first build’ approach minimizes risks by integrating security measures from the very beginning of the new platform’s development. This proactive strategy ensures that security is an inherent feature, not an add-on, leading to a more resilient system less prone to vulnerabilities during migration and more resistant to attacks post-launch. This phase involves rigorous testing, including penetration testing and vulnerability scanning, before the launch to identify and rectify security flaws.
Developing the new platform securely means integrating security at every layer, from the code itself to the server configurations. This prevents common vulnerabilities like SQL injection or cross-site scripting (XSS). Creative engineering from 360Locker ensures that the new e-commerce solutions are not only secure but also scalable and high-performing.
**Penetration testing** is a simulated cyberattack against a computer system to check for exploitable vulnerabilities. This proactive testing identifies weaknesses before malicious actors can exploit them. **Vulnerability scanning**, on the other hand, uses automated tools to identify potential security weaknesses in applications and systems. Both are crucial steps to harden the new environment.
User Acceptance Testing (UAT) should include a specific focus on security features. This involves testing how users interact with security aspects, such as login processes, payment gateways, and data privacy settings. Performance testing under various loads ensures the new platform can handle high traffic volumes without compromising security or speed, which is vital for e-commerce.
Finally, setting up robust monitoring and incident response systems is crucial. These systems detect suspicious activities in real-time and provide protocols for immediate action in case of a security breach. 360Locker’s expertise ensures these systems are fully integrated, providing comprehensive protection for the new e-commerce platform.
Phase 4: Go-Live and Post-Migration Security
Minimizing downtime during the final cutover is essential to prevent business disruption and revenue loss. This involves careful scheduling and precise execution of the migration plan. Once live, verifying data integrity post-migration is critical to confirm that all data has transferred accurately and completely to the new secure e-commerce platform.
What role does continuous testing and monitoring play in a secure e-commerce migration? Continuous testing, encompassing penetration testing and vulnerability scanning, is crucial before launch to identify and rectify security flaws. Post-migration, continuous monitoring and threat detection systems are vital for real-time security, ensuring ongoing protection and rapid response to any emerging threats or breaches. Implementing continuous security monitoring and threat detection ensures ongoing protection against new and evolving threats. This involves using tools that can identify anomalies, malicious traffic, and unauthorized access attempts in real-time.
Regular security audits and updates are non-negotiable. Software vulnerabilities are frequently discovered, making it necessary to apply patches and updates promptly. For instance, according to CVE Details, thousands of new vulnerabilities are reported each year, highlighting the need for vigilance. This proactive maintenance keeps the platform resilient against emerging threats.
Backup and disaster recovery planning are also vital components of post-migration security. Regular backups ensure that data can be restored quickly in case of a system failure or cyberattack. A robust disaster recovery plan outlines the steps to recover business operations with minimal disruption. 360Locker offers 99.95% uptime hosting, ensuring that business operations remain consistently available and secure. Their 24/7 support provides ongoing assistance, addressing any security concerns promptly.
360Locker’s Advantage: Your Partner in Secure E-commerce Migration
360Locker offers a distinct advantage for businesses undergoing secure e-commerce migration, especially for newcomers in the web world. Their “security-first build” philosophy ensures that cybersecurity is integrated into every stage, from concept to deployment. This holistic approach significantly reduces risks compared to solutions where security is an afterthought.
With over 500 clients served and 120+ projects delivered since its founding in 2020, 360Locker demonstrates a proven track record. Their average delivery time of 30-60 days highlights efficiency without compromising quality or security. They also offer free website migration, a significant benefit that reduces the financial burden and complexity for businesses transitioning platforms.
360Locker’s creative engineering ensures not just security, but also scalable and robust digital solutions tailored to specific business needs. Their 24/7 support means clients receive immediate assistance, which is crucial for maintaining continuous security and operations. This, combined with affordable pricing, makes robust and secure e-commerce solutions accessible to a wider range of businesses.
The company caters specifically to businesses seeking secure, scalable digital solutions, including e-commerce platforms. Their sister concern, ITpreneurs.Tech, further expands their capabilities, providing broader tech expertise that complements 360Locker’s specialized focus. This integrated approach offers comprehensive support for any digital transformation journey.
Looking Ahead: E-commerce Security Trends Beyond 2026
Beyond 2026, e-commerce security will continue to evolve rapidly. What future security trends should e-commerce businesses prepare for beyond 2026? Beyond 2026, e-commerce businesses should prepare for the increased role of AI and machine learning in cybersecurity, the adoption of passwordless authentication, enhanced supply chain security, and the emerging threats posed by quantum computing. Embracing these advancements will be crucial for maintaining robust protection.
The role of AI and machine learning in cybersecurity is expanding. These technologies will become even more adept at identifying complex attack patterns and predicting potential threats, offering proactive defense mechanisms. According to IBM’s 2023 Cost of a Data Breach Report, AI and automation significantly reduce the average cost of a data breach.
Passwordless authentication and enhanced Multi-Factor Authentication (MFA) are gaining traction. Technologies like biometric authentication or FIDO-based security keys will offer more secure and convenient login experiences, reducing the risk associated with traditional passwords.
Supply chain security for e-commerce is another critical area. Businesses must scrutinize the security practices of all third-party vendors and partners to mitigate risks stemming from interconnected systems. A single weak link in the supply chain can compromise an entire operation.
Finally, preparing for quantum computing threats is a long-term but essential consideration. Quantum computers have the potential to break current encryption standards, necessitating the development of post-quantum cryptography. While still emerging, businesses should begin understanding its implications and potential solutions. Continuous adaptation to these emerging threats is the only way to ensure enduring secure e-commerce migration and operations.
Frequently Asked Questions
What are the non-negotiable security considerations for e-commerce migration in 2026?
Non-negotiable security considerations include end-to-end data encryption (in transit and at rest), robust access controls, continuous security monitoring, regular penetration testing, and strict adherence to compliance standards such as PCI DSS, GDPR, and CCPA.
How can businesses ensure data integrity and prevent data loss during an e-commerce platform transition?
Businesses can ensure data integrity and prevent loss through secure data extraction methods, encryption of all data, implementing strong access controls, thoroughly sanitizing and validating data for the new platform, and maintaining comprehensive backups.
What role does continuous testing and monitoring play in a secure e-commerce migration?
Continuous testing, including penetration and vulnerability scanning, identifies weaknesses before launch, while ongoing monitoring after go-live detects and responds to threats in real-time, ensuring sustained security and system integrity.
How can a 'security-first build' approach minimize risks during and after migration?
A 'security-first build' approach integrates security measures from the initial design phase, minimizing vulnerabilities by baking security into every layer of the new platform, thereby reducing the likelihood of breaches during and after migration.
What compliance standards (e.g., PCI DSS, GDPR) must be considered for secure e-commerce migration?
Key compliance standards to consider include PCI DSS for payment data security, GDPR for data protection in the EU, and CCPA for consumer privacy in California, ensuring legal adherence and customer trust.
What future security trends should e-commerce businesses prepare for beyond 2026?
Beyond 2026, e-commerce businesses should prepare for the increased role of AI and machine learning in cybersecurity, the adoption of passwordless authentication, enhanced supply chain security, and the emerging threats posed by quantum computing.